This list was written in 2022. The eight practices below still apply in 2026. The market and attack figures stay labeled with the year they were reported.
A Statista forecast cited when this was written put worldwide mobile app revenue near $693 billion in 2021 and projected $935 billion by 2023. Those numbers are that forecast, not a 2026 market size. The growth came with cyberattack risk, which is why mobile app security still matters.
In Check Point’s Mobile Security Report 2021, 97% of organizations had faced a mobile-related attack, and 46% of employees had downloaded at least one malicious application. Those are 2021 figures. People exchange data with brands inside apps, and weak security exposes that data.
These are the practices to use.
- Data encryptions
- Secure codes
- User authentications
- Compliance and integrity
- Secure APIs
- Security triggers
- Data privileges
- Secure containers
1. Data Encryptions
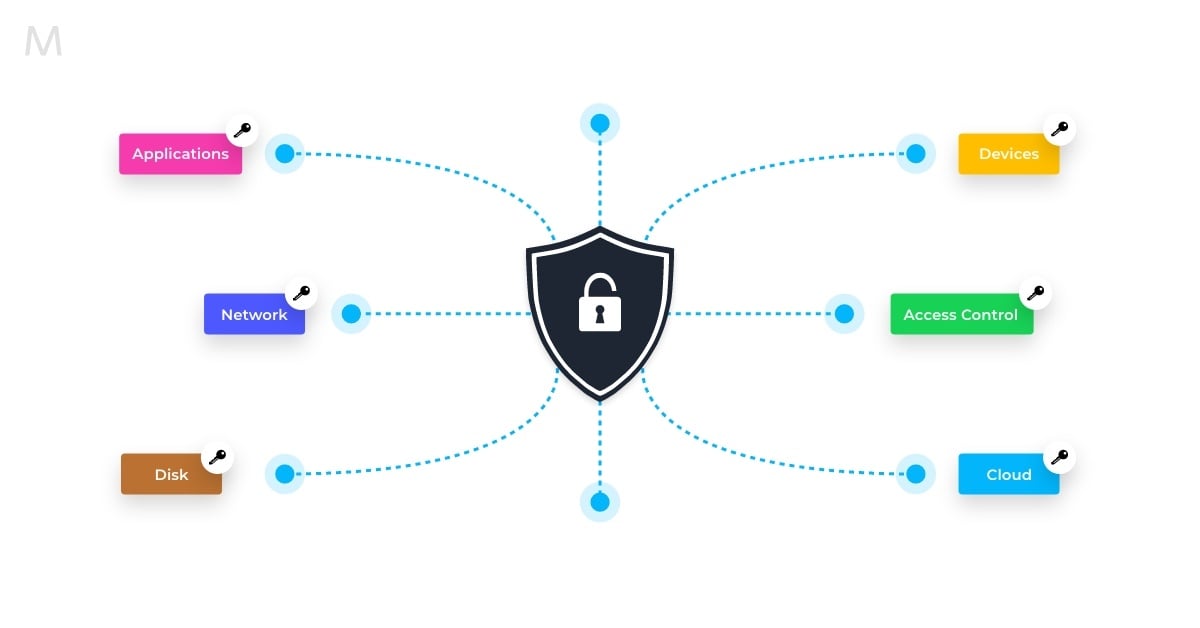
Lots of applications are used by several users across devices and operating systems. You need to make sure the data exchanged over the application is not exposed because of a weakness in an operating system or a device.
One way to do this is by encrypting the data across applications. Encryption scrambles the data so it is unreadable to an attacker. There are two ways to encrypt data:
- Symmetric encryption
- Asymmetric encryption
Symmetric encryption uses the same security key to encrypt and decrypt data. Asymmetric encryption uses different keys. The next practice, for mobile app security, is secure coding.
2. Secure Codes
Every application is built on pieces of code. Secure code is extremely important for mobile app security.
An IT Pro Portal report cited when this was written found that 82% of vulnerabilities appear in application source code. That 82% is from the report, not a 2026 count. The source code still has to be free of the bugs an attacker can use.
Hiring a professional app designer is one way to get that review. Testing the application is the other: look for bugs before someone else does.
3. User Authentications
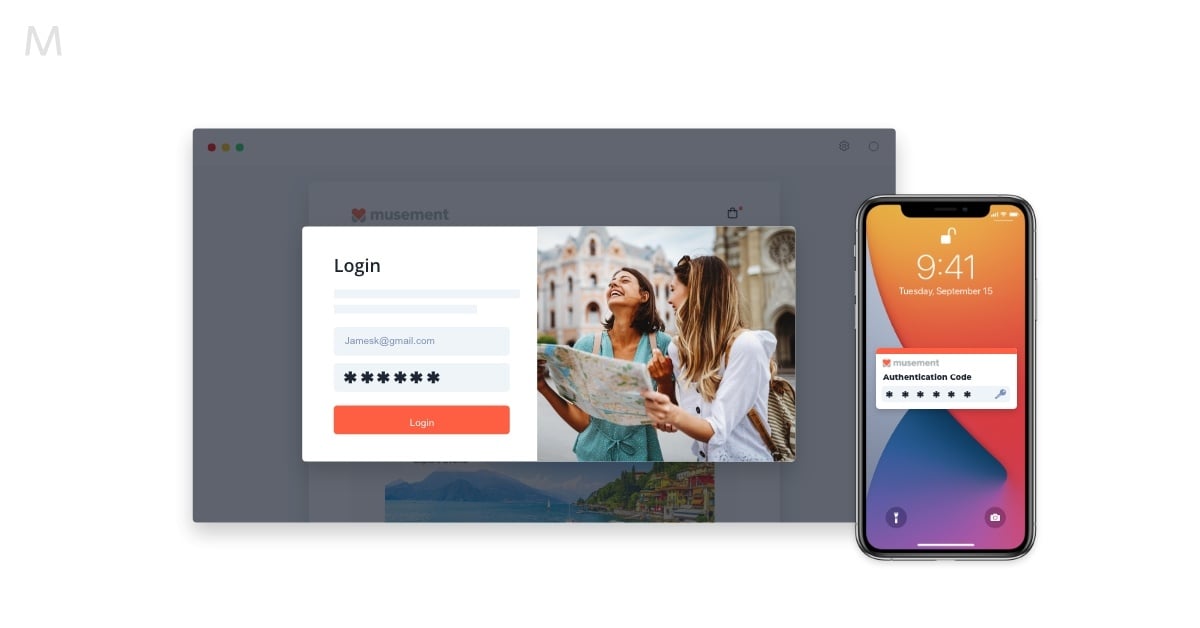
Mobile applications collect a lot of user-generated content. Without authentication, that content and the account behind it are open to attack. Social engineering is a common way in. Once an account is taken over, injecting something malicious through user-generated content is easier.
Use more than a password. Multi-factor authentication adds a one-time password, a token, or a security key. A two-factor flow, for example, asks the user to confirm an OTP on the device.
4. Compliance and Integrity
When a mobile app is launched, it has to meet security requirements. App stores set rules for download and installation.
Modern smartphones distribute signed apps. Signing is how a platform limits distribution to applications that have been checked. Developers submit the app, and the store checks their identity and the app’s security requirements. If the app matches the operating system’s guidelines, it can be downloaded.
Code signing is what proves the code has not been changed since it was signed and that it comes from a known publisher. A code signing certificate is one way to do that. The certificate carries the publisher’s identity, which users can check with the public key.
5. Secure APIs
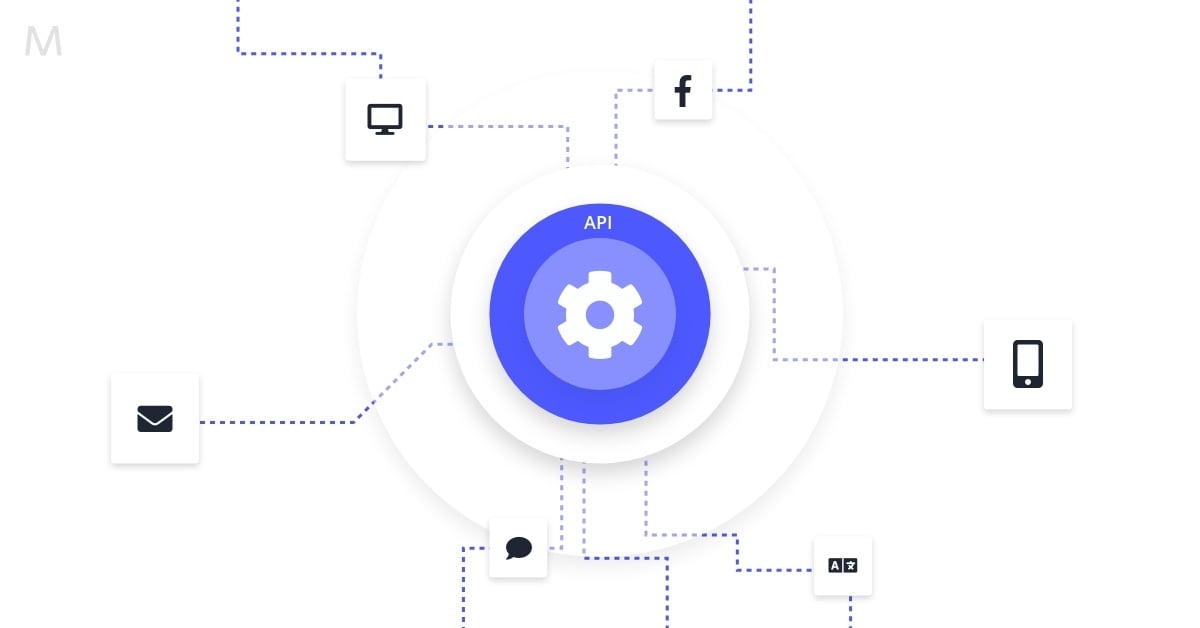
APIs connect third-party services and let different systems exchange data. A secure API does not leave that data open. Authorize who can read it.
6. Security Triggers
Use triggers that alert you when the application source is tampered with. AWS Lambda functions are one way to raise an alert for tampering or a malicious injection in a cloud application.
7. Data Privileges
Give sensitive data to as few people as possible. Least privilege keeps that data away from someone who should not have it.
8. Secure Containers
Security keys are part of encryption. Avoid storing those keys only in a local data center. Where sensitive information does sit in a local data center, use a secure container for the keys. Protocols such as 256-bit AES, with SHA-256 for hashing, are the usual way to protect them.
Protect your Business
Mobile application security belongs on the priority list. Social engineering and malicious injection are still how attackers take over an application. The measures above are how you keep that data, and the people who share it, out of reach.